Information Security Officer · Focus on European defence regulation

An ISMS that survives the audit. Regulation that holds.

Information security and compliance grounded in audit practice, with a focus on European defence regulation. I translate NATO, EU and national requirements into decisions a board can act on.

Into the workshop Defence & regulation
01 Audit practice An ISMS that convinces auditors: under ISO 27001, NIS2 and TISAX. Demonstrably effective, not merely documented.
02 Pragmatism Security without bureaucracy. Feasible, proportionate and fitted to the organisation.
03 Built, not just read I do not only check standards on paper, I check them in a build of my own. What came out of it is in the workshop.
04 EU regulation NIS2, DORA and the AI Act apply across the EU. I translate them into decisions a board can act on.
Separation is architecture AI does not write without a signature A framework is content, not schema Maturity, not traffic lights Effective beats documented Compliance is not filing Separation is architecture AI does not write without a signature A framework is content, not schema Maturity, not traffic lights Effective beats documented Compliance is not filing

01 - Practice

Four rulebooks. One management system.

01

Defence & European regulation

NATO, EU and national requirements for defence suppliers: quality assurance, classified information and export controls, sorted by what contract, jurisdiction and classification level actually trigger.

See the overview →
NATO AQAP EUCI VS-NfD
02

Information security & ISMS

Management systems under ISO 27001, BSI IT-Grundschutz and TISAX: how they come about, how they avoid rotting in daily operation, and what internal audits ultimately measure them against.

ISO 27001 IT-Grundschutz TISAX
03

Compliance & regulation

NIS2, DORA and critical-infrastructure rules: what they actually demand, where they overlap, and why compliance can be a strategic strength rather than a chore.

NIS2 DORA KRITIS
04

AI governance & EU AI Act

Governance frameworks and risk management for AI adoption under ISO 42001, and where the AI Act meets an existing ISMS. I do not only check that on paper, I check it in a build of my own. See the workshop.

ISO 42001 EU AI Act Policy

02 - Hands-on

I do not only review documents.

Management systems are not built at a desk alone. These are the areas I work on myself — technical as well as organisational.

Internal audits

Under ISO 27001, NIS2 and TISAX. As the auditor, not as the supplier of evidence.

Cyber risk assessments

Assessing exposure and control effectiveness rather than handing out traffic lights.

IT security concepts

Under BSI IT-Grundschutz, including critical-infrastructure environments and public authorities.

ITSCM & BCM

Continuity and recovery plans that hold when it matters — plus awareness training.

AI in information security

Responsible for the secure adoption of AI inside a running ISMS.

Hands-on offensive practice

Ongoing technical training on TryHackMe. Profile publicly visible.

View profile ↗

03 - Workshop

I test my theses by building them.

No offer, no product. A test rig I use to check whether a standard holds up once you force it into a data model. Four things it taught me.

01

Separation is architecture, not policy.

A group-wide ISMS has to keep subsidiaries and sites properly apart. In my build every table carries the organisation as a mandatory field, and every access path runs through exactly one control point. If you only check separation in application logic, you do not have it.

organization_id  uuid  NOT NULL
// on every table. no exceptions.
02

AI may read. Writing needs a signature.

Read tools run automatically, writing tools never without human approval, and every AI-drafted record stays visibly flagged. That is the human oversight the AI Act demands, as code rather than as a statement of intent.

tool.read   ->  auto
tool.write  ->  approval + audit_log
03

A framework is content, not schema.

Adding SOC 2 or NIS2 must not trigger a database migration. Build your model on a single standard and you build yourself into it, which you only notice when the second one arrives.

frameworks/soc2.seed.ts
// new standard = new file
04

Maturity, not traffic lights.

Red-amber-green tells a board nothing, because it has no direction. A maturity level tells them where the organisation stands and what the next step costs.

maturity: 0..5
// not: red | amber | green

04 - Profile

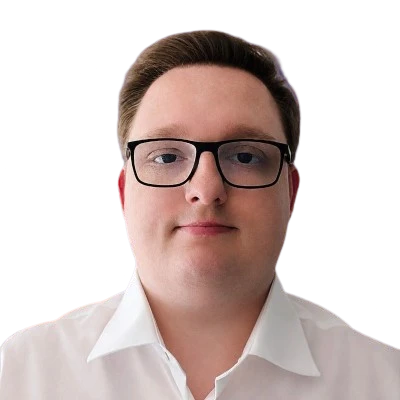
Konstantin Meyering

Information Security Officer with a background in data science. I combine classic security management under ISO 27001 and the German BSI IT-Grundschutz with AI governance under ISO 42001, from federal agencies to international groups. Advisory board member at Global Cyber Circle, author of "Navigating NIS-2".

Konstantin Meyering, Information Security Officer
IT-Grundschutz-Praktiker Ethical Hacker Fortinet Cybersecurity Global Cyber Circle
2026–present

Information Security Officer · Amadeus Fire

Running ISMS under ISO 27001, NIS2 and TISAX. Internal audits, cyber risk assessments, ITSCM, the CISO mandate for group companies, and responsibility for AI in information security.

2025–present

Advisory board · Global Cyber Circle

Focus on cyber & regulation: NIS2, DORA and compliance as a strategic strength across the DACH network.

2023–2026

Information Security Consultant · DS DATA SYSTEMS

Security analyses under ISO 27001 and BSI IT-Grundschutz, ISMS implementations, BCM and data protection for companies and public authorities.

2022–2023

Junior IT Consultant · Grouplink IT Solutions

ISMS implementation under ISO 27001, security concepts under BSI IT-Grundschutz / critical infrastructure rules, security awareness training.

05 - Contact

Let us talk as equals.

Questions on ISO 27001, NIS2, DORA, ISO 42001 or the EU AI Act? I welcome messages, in English or German.

meyering@zoxai.de LinkedIn